 Checkcraft
Validate required and unexpected JSON fields
Checkcraft is a desktop app for checking APIs and logs without code, with a free edition. Download, no sign-up →
A contract can fail in two different ways. A required field can disappear, or a service can return a property that should not be exposed. These need separate checks.
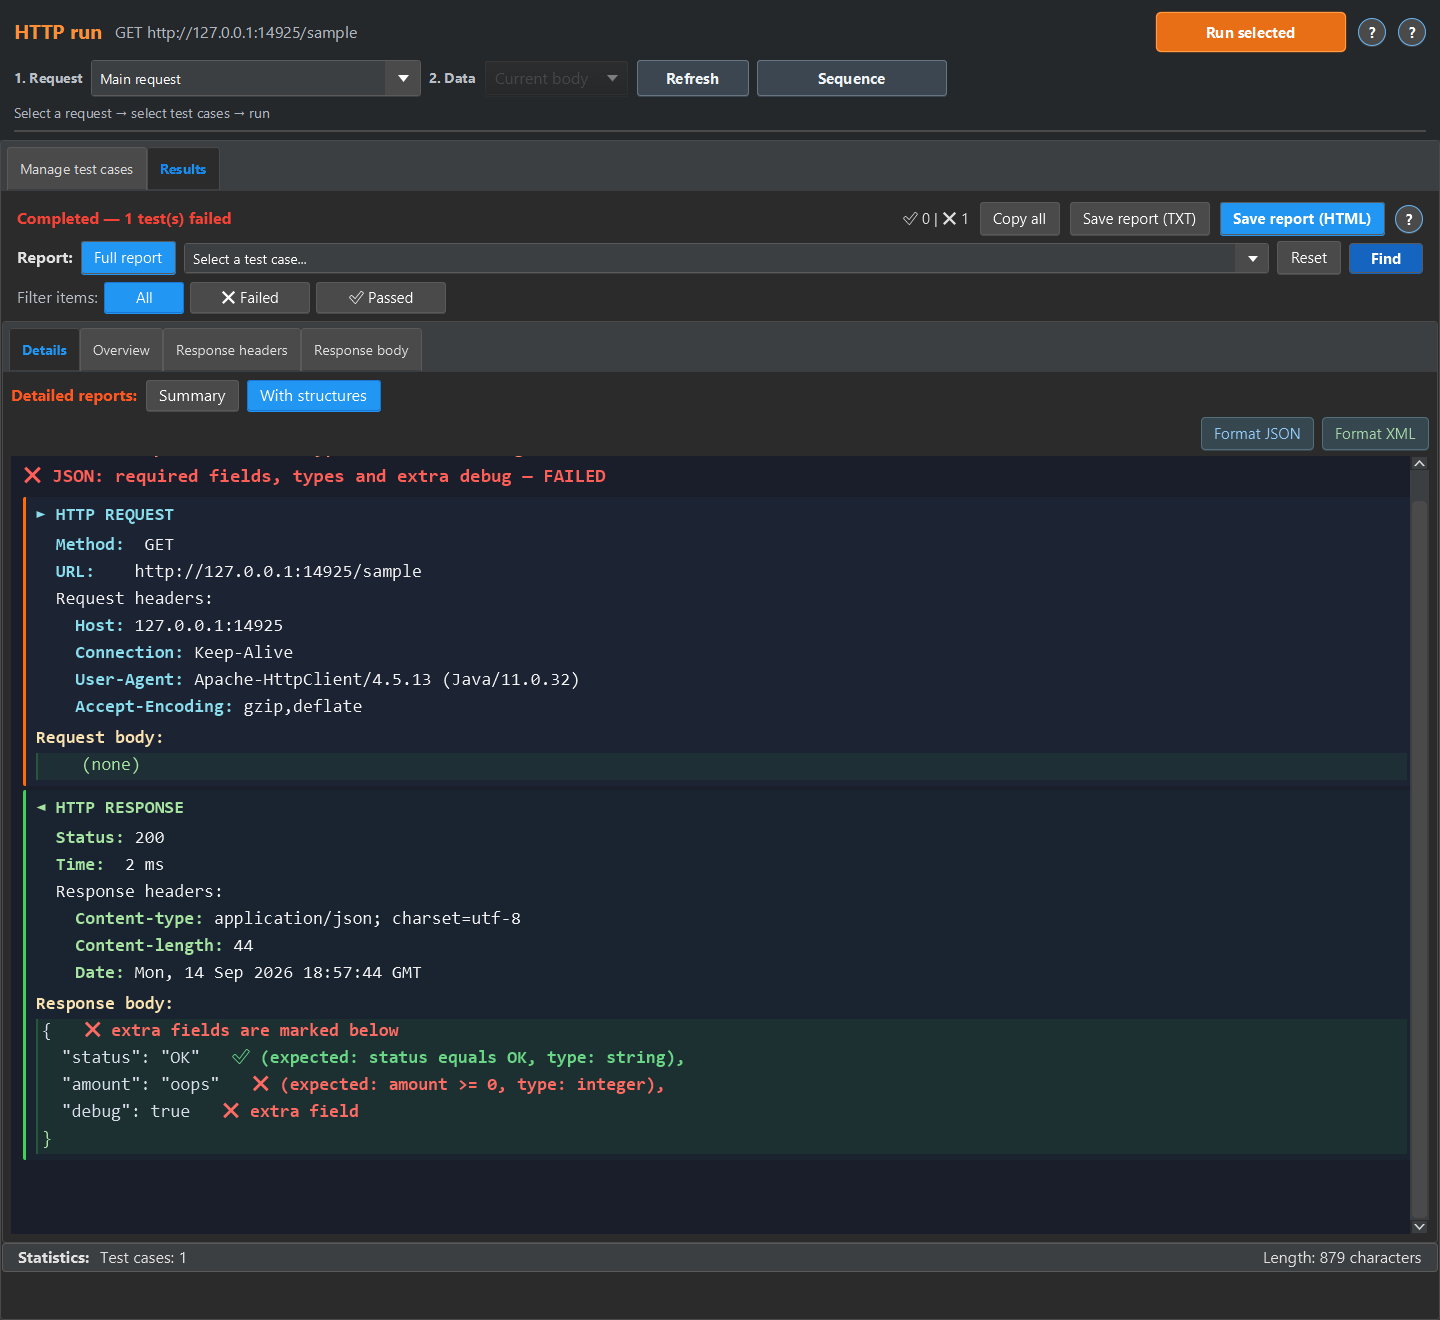
The test checks required values and rejects an unexpected property. Its broken input demonstrates a real failure.
Check required fields explicitly
Add a JSON field rule for each required path. Choose notEmpty when an empty value should also fail. Use a value comparison or type check where the requirement calls for one. Being listed in an allowed-field list does not make a field required.
Use a whitelist for extra properties
The JSON Whitelist step defines allowed keys at a chosen object path. Add separate rules for nested objects. Keep the contract precise rather than generating the allowed list from every response, which would silently accept newly introduced properties.
Test both failure directions
Remove a required field from one copy of the input. Add an extra property to another. Run the unchanged test case on each. The report should explain each failure. If a field is optional, do not accidentally make its absence an error.
Repeat the check with ready-made files
The quick experiment below runs in the test case editor. The screenshots show the detailed report available in HTTP run or Log run. For HTTP run, return the sample JSON or XML from a local mock and run the imported case against it, then open Results, Details and With structures. For Log run, load the sample into a log source, enable No request, run the case, then open Details and Detailed.
Download the Checkcraft test case and two inputs. One input is valid, and the other contains a deliberate error. These synthetic examples are available without registration.
Run the example in Checkcraft
Create a collection, a check and a test case using the workspace tree context menu. Click Import in the test case editor and choose the downloaded test case. Open the added case, copy the valid JSON, click Paste data for analysis, then Run test case. Open Result to inspect the report.
Repeat with the broken JSON without changing the rules. The first run should pass and the second should fail. If you see a different outcome, check the selected data source, imported steps and report.
The example files were executed against the application source on 14 September 2026. Reference reports in English are available for the passing run and failing run. Sample names and literal data values do not change when you switch the interface language.
Check unwanted fields without claiming a security audit
A whitelist can detect a key outside an agreed response shape, such as an unexpected debug field. This can help catch excessive data exposure in that response. It does not scan an API for every vulnerability or replace AppSec and penetration testing. Sensitive data requires explicit requirements and review of exported reports.
See the result on a small example first
Start with the sample, inspect the failure and then try a sanitized example from your own API. Free is available for Windows and Linux with no time limit.
Download FreeDownload and first runNo sign-up or email needed, the archive is ready in a couple of minutes. See the edition limits.